Critical
Immediate exploitation risk, active in the wild
Zupitrix
Surface risk before attackers do
Zupitrix runs deep technical audits across applications, APIs, cloud infrastructure, identity systems, and data stores — delivering prioritized findings, verified impact, and remediation guidance your engineers can act on immediately.

Severity model
Immediate exploitation risk, active in the wild
Exploitable with moderate effort, significant impact
Requires specific conditions, contained blast radius
Informational or hardening recommendations
Audit scope
OWASP Top 10 plus business logic abuse, auth/session hardening, CSRF/XSS, file handling, and sensitive-data exposure across web + mobile.
REST + GraphQL authZ, rate limiting, object-level access control (BOLA), schema validation, mass assignment, and data leakage — with reproducible requests.

IAM policy risk, network exposure, storage misconfiguration, logging gaps, and guardrail coverage across AWS/Azure/GCP — mapped to CIS where relevant.
SSO + conditional access, MFA coverage, privilege escalation paths, service accounts, and federation trust chains — with least-privilege remediation paths.
Segmentation, firewall/security groups, DNS security, VPN/ZTNA posture, and lateral movement paths between zones — validated with reachability checks.

Encryption at rest/in transit, key management + rotation, backup security, data classification, retention/deletion controls, and access logging for regulated data.

Deliverables
Risk posture overview with severity distribution and top-5 business-critical findings for leadership.
Detailed reproduction steps, evidence screenshots, affected endpoints, and remediation code samples.

Prioritized finding list with owner fields, SLA targets, and status columns ready for Jira or Linear import.

Annotated diagrams highlighting trust boundaries, data flows, and where controls are missing or misconfigured.
Methodology

Define audit boundaries, threat model, compliance drivers, and success criteria. We align on what “critical” means for your business and users.

Enumerate assets, map data flows and trust boundaries, review architecture + IaC, and identify high-value targets worth a deeper manual pass.

Execute test plans across all in-scope domains — automated scanning plus manual expert review focused on authZ, data access, and real exploit chains.
Correlate findings into attack paths, assess exploitability + blast radius + business impact, and assign severity with context your stakeholders can trust.
Deliver an executive summary, a technical report with reproduction steps, and a remediation tracker ready for Jira/Linear — with fix guidance and owners.
Verify remediations, update finding statuses, and issue a clean delta report. Critical/high items get re-tested with the same exploit path.
Industry focus

PCI-DSS aligned audits covering cardholder data flows, tokenization, and third-party integrations.
PCI · SOC 2 · DORA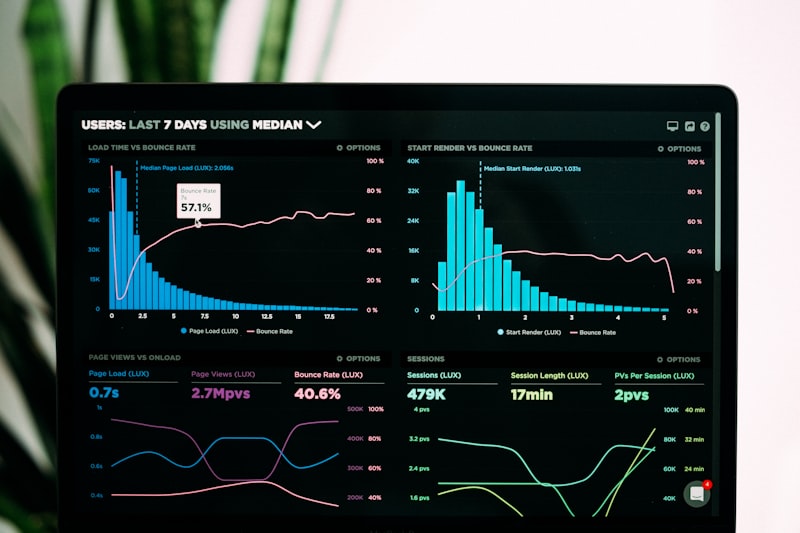
HIPAA-aligned reviews of PHI handling, access controls, audit logging, and vendor risk.
HIPAA · HITRUST · FDA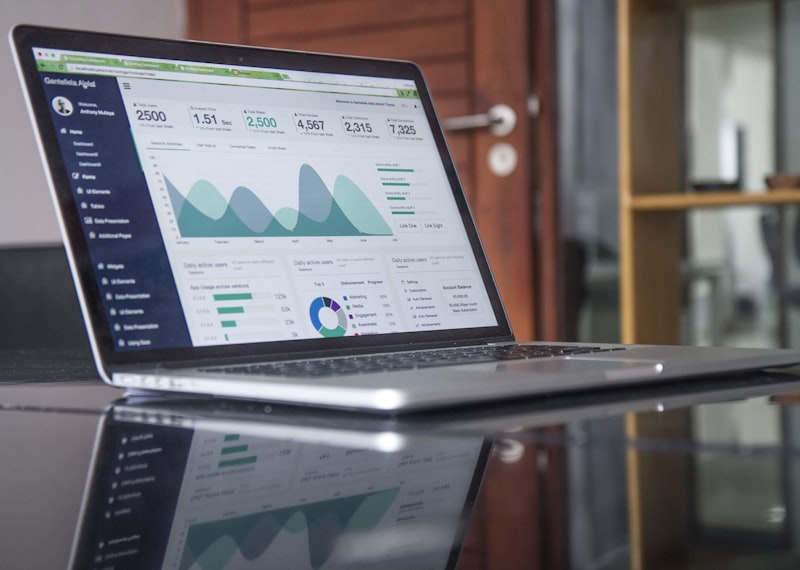
Multi-tenant isolation, API security, CI/CD pipeline hardening, and customer-facing security posture.
SOC 2 · ISO 27001What you receive
Risk-ranked findings with CVSS + business context scores
Executive summary with severity heat map
Technical report with reproduction steps
Remediation tracker importable to Jira / Linear
Architecture diagrams with annotated trust boundaries
Re-test report confirming remediation effectiveness
Outcomes
Severity-ranked backlogs mean engineering fixes what matters first, not what's loudest.
Executive summaries translate technical findings into business risk language leadership understands.
Audit reports map to SOC 2, ISO 27001, and HIPAA controls — ready for auditor review.
Stack & tooling
The audit blends automation with expert validation — using best-in-class scanners, code analysis, and cloud posture tooling to turn signals into verified, fixable issues.
Manual testing and request replay to validate exploitability.
Baseline scanning for common web and API exposures.
Dependency and container vulnerability detection with fix guidance.
Image, dependency, and IaC scanning for cloud-native estates.
Container surface review for privileged configs and insecure defaults.
CIS-aligned cluster hardening and workload exposure checks.
Account posture review for IAM, storage, and network exposure.
Codified control checks so misconfigurations are caught before deploy.
Zupitrix role
Zupitrix owns the audit scope, execution, and reporting end-to-end — balancing automated coverage with expert manual validation. We partner with your engineers on remediation planning, verify fixes through re-testing, and help you translate findings into measurable risk reduction.

FAQ
Keep exploring
Let's build something amazing together. Contact us to discuss your project and see how we can help bring your vision to life.
Fill in the form and we'll respond within one business day — personally, not with a template.


